Understory ranks No. 140 on Inc. 5000 list of fastest-growing companies in U.S. Read more about Understory on the 2026 Inc. 5000 list

George Kurtz

George Kurtz

President / CEO & Founder at CrowdStrike

San Jose, California, United States · Cybersecurity · LinkedIn profile

George Kurtz is President / CEO & Founder at CrowdStrike, based in San Jose. On LinkedIn George writes mostly about company news and team and hiring, most often as text posts.

120K+followers
1.6Kreactions on a typical post
2.6Kreactions on the best post
2 of 30recent posts worth featuring

George's best LinkedIn posts

Recent posts that drew 100 reactions or more and say something a peer would learn from, most reactions first. Click any post to open it on LinkedIn.

George Kurtz
George KurtzPresident / CEO & Founder at CrowdStrike
I read Dario Amodei's essay calling on the labs to pace the frontier. Sam Altman agreed. The frontier will move at whatever speed it moves. The rest of the world will not slow down. Our job in the cybersecurity community is to make sure it moves securely and safely. Here’s what I see from the front lines: 1. The unit of threat is no longer the hacker. It's an autonomous campaign. I call it the Agent-state. We see coordinated AI agents executing attack campaigns at machine speed. 2. Sophistication is dead as an attribution signal. AI gives every criminal and lone actor elite execution. Identity, infrastructure, and intent tell you who's behind an attack. Skill doesn't. 3. Runtime is the control point. Endpoints, cloud workloads, and SaaS are the battleground. Governance documents don't stop an agent in motion. Enforcement at machine speed does. 4. Every AI agent is a privileged identity. Least privilege, short-lived credentials, traceable actions, and a kill switch. Permissions never expand because an agent decides it needs more. 5. Defense has to be autonomous but also bounded. Machine-speed response, tiered by consequence, with humans owning the high-impact calls. 6. Every failed attack should make every defender smarter. Feed what we block back into detection, across customers and models, with privacy intact. This is what CrowdStrike and NVIDIA introduced with SafeMind: an agentic, always improving model and harness protection system built for defenders. 7. The AI industrial base is critical infrastructure: weights, training clusters, APIs. Call it what it is and protect it like it is. Pacing what comes next doesn't secure what's already here. The credible path is to deploy with proof: board-level accountability for AI security, independent external red teaming, incident disclosure, secure defaults, and controls that work in production - not on paper. Anthropic and OpenAI just committed to embedding independent evaluators with employee-level access. CrowdStrike will bring what we see from the front lines to that table. The ability for AI to act must be matched by the ability for defensive AI to stop the breach. https://lnkd.in/ggY5edWX
George Kurtz
George KurtzPresident / CEO & Founder at CrowdStrike
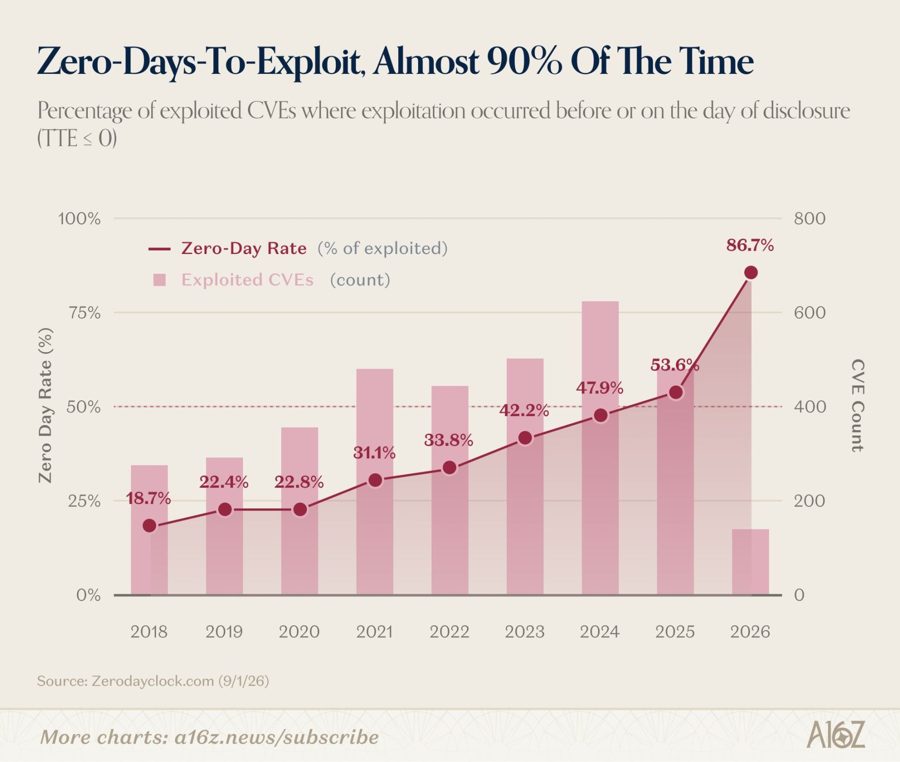
As defenders, you need to look at your watch, not a calendar. PHP2Shell is a big one. Here are my takeaways.   1. These flaws reach back more than a decade. PHP’s maintainers identified one underlying problem in 2024, but its full impact wasn’t clear until AI-assisted research demonstrated its exploitability. What seems impractical to exploit today could easily be exploitable tomorrow as models advance. 2. Much of the web runs on PHP, and a lot of it is on versions that are out of support. Some get a source backport you must build yourself. Some get nothing. Attackers aren't hunting the servers you just patched. They're hunting the ones you forgot you own. There is going to be a very long tail on remediating these vulnerabilities, and we will see many downstream breaches over the coming months.   3. The patching window has completely collapsed. While we’ve exponentially found more vulnerabilities and exponentially created more patches, we’ve hit the sound barrier on operationally rolling them out. Even more concerning is the increase in exploitation occurring before or on the day of disclosure. When a flaw gets exploited, almost 90% of the time it’s hit on or before the day it’s disclosed.  4. Coordinated disclosure in open source is really hard. It runs on trust, not contracts. There were many people in the loop, and for good reason. Lots of great people doing incredible work. However, I expect leaked disclosures will be the norm, not the exception, as we move forward in the Agent-state era. CrowdStrike has coverage in place to protect customers. Patching and upgrading vulnerable PHP versions should be the immediate priority.  https://lnkd.in/gsbDqirR The Andreessen Horowitz chart below says it all.
Image from George Kurtz's LinkedIn post

What George posts about

  • Company news50%
  • Team and hiring20%
  • Industry analysis17%
  • Events and content10%
  • Personal stories3%

What makes the best ones work

  • Most of George's best posts open with a plain statement of a view.
  • 50% of them are text only, with no image or video.
  • They run long, often past a thousand characters.

Questions about George Kurtz

Who is George Kurtz?

George Kurtz is President / CEO & Founder at CrowdStrike, based in San Jose. On LinkedIn George writes mostly about company news and team and hiring, most often as text posts.

What does George Kurtz post about on LinkedIn?

Mostly company news, team and hiring and industry analysis. Of the 30 recent posts we read, 2 drew 100 reactions or more with real substance.

What is George Kurtz's most popular recent LinkedIn post?

The one that opens “I read Dario Amodei's essay calling on the labs to pace the frontier. Sam Altman agreed. The frontier will move at whatever speed it moves.…”, with 2,638 reactions and 147 comments.

Every post belongs to George Kurtz. Understory is not affiliated with George Kurtz or CrowdStrike. We read public LinkedIn posts to study what B2B leaders write and what their audiences respond to, and the bio is our own summary. If this is you and you would like the page changed or removed, email alex@understoryagency.com and we will do it.

More cybersecurity thought leaders

See every cybersecurity thought leader, or the ads CrowdStrike runs.

Want posts like these on your profile

We ghostwrite LinkedIn posts for B2B founders and executives, in their own voice, and turn the audience into pipeline.